CFPB can't confirm abandoned office kit is secure, watchdog alert says
The US Consumer Financial Protection Bureau has told its inspector general it cannot confirm whether IT equipment left behind in four closed offices, or any data on it, is secure, in an urgent management alert issued on Wednesday.
 Dr. Amara PatelEconomy, business and world
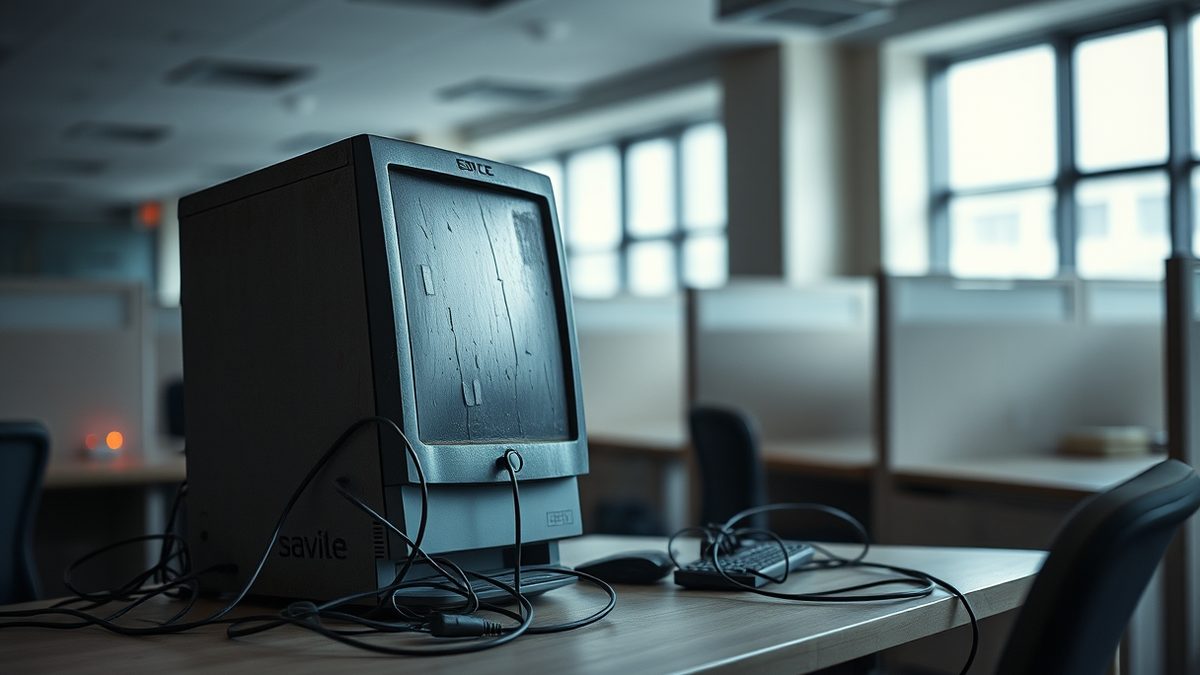
The warning, first reported by Bloomberg's J.J. McCorvey, covers hardware abandoned when the bureau ended leases on its New York, Chicago, San Francisco and Atlanta offices in early 2025. The inspector general for the Federal Reserve Board and the CFPB found the problem during its yearly cybersecurity audit.
The watchdog wrote that the CFPB has "no way of knowing" whether anyone accessed, changed or removed the hardware, or any sensitive data on it. It warned the kit could hold consumer complaints, financial details and confidential supervisory records.
Sixteen months, no plan
The timeline is documented in the alert. The CFPB rented the offices from the General Services Administration, which took over physical security when the leases ended in February 2025. The bureau stopped paying for the offices' network links that September. By March 2026 it still had not fully moved out. In June, officials told auditors nobody had checked the equipment. In September, they said there was still no approved plan or timeline, citing litigation and travel approvals.
The bureau agreed to find and secure all the equipment, but rejected the idea that it faces a higher breach risk, in a letter dated 18 September. "No databases containing sensitive data are housed in the regional offices," chief information officer Christopher Chilbert wrote. He said the kit was mainly used for networks, internet access and admin work. The bureau has started clearing out the IT at each former office, one site at a time, and aimed to finish by 30 September.
The closures were ordered by Russell Vought, who was running the bureau at the time. Staff were told to stop work and stay home in February 2025, soon after Donald Trump returned to office. Since then the CFPB has scaled back oversight of banks and lenders and dropped enforcement cases worth hundreds of millions of dollars. The administration plans to cut half of its remaining 1,100 staff, according to Bloomberg. States have tried to fill the gap: in July, 46 states settled with Block over Cash App fraud claims, a type of case the bureau once led.
That retreat matters for the wider question in this story. Data protection enforcement in the US has always leaned on a mix of federal agencies, state attorneys general and private litigation. When one agency stops investigating and also loses track of its own hardware, the practical effect is a thinner safety net, not a single dramatic failure.
France: seven weeks of silence
The most detailed recent enforcement post-mortem comes from France. An attacker used stolen passwords of staff at the DGFIP, the tax administration that runs impots.gouv.fr, to take tax data on hundreds of thousands of taxpayers and businesses in June and July. Neither the tax administration nor the national cybersecurity agency, ANSSI, saw the data leave. ANSSI's report, published on Tuesday and covered by The Hacker News, says the attack was not sophisticated: it worked because of weak login protection, poorly separated networks and gaps in monitoring.
The numbers are specific. The stolen data covers a little over 350,000 individuals and a little over 250,000 businesses, the DGFIP says. Taxpayers' own online accounts and passwords were not compromised. For individuals, the data that may have been viewed or copied includes tax ID, contact details, family situation, reference taxable income and withholding rate, plus a list of messages exchanged with the DGFIP. For fewer than 250 people, the messages themselves may have been taken. For businesses, the haul covers company name, SIREN registration number, address and basic message details; for fewer than 2,076 businesses, message content may have been seen.
The theft became known on 12 August, when the attacker claimed it on an online forum, seven weeks after the first batch was taken. Prime Minister Sébastien Lecornu then asked ANSSI for an in-depth audit. In August, the ministry overseeing the DGFIP offered a different explanation, saying access checks had not revealed the theft "because of the sophistication of the attack", a claim the agency report now contradicts. The attacker used two routes. The first began with suspicious logins in early May and relied on several dozen DGFIP staff passwords stolen over three months, probably by infostealers on machines the DGFIP did not manage. Two portals, PIGP and ADER, asked only for a password. The attacker reached the government network RIE through compromised Education ministry systems, and sensitive DGFIP applications were not separated from the rest of that network. The second route went through APEX, a partner portal used by notaries and land surveyors, and a compromised surveyor's computer may have let the attacker bypass a one-time code.
Fines arrive, data still moves
Regulators elsewhere are moving on penalties, with mixed signals on scale. On 21 September, Ireland's data protection watchdog fined Google 403 million euros over improper use of location data, a decision reported across multiple outlets including Lawxy AI and Compliance Week. The same week, the European Data Protection Board opened consultation on a new GDPR fining framework, with Pinsent Masons reporting that future fines are set to be more equal across the EU. Smaller cases show the same machinery running at national level: Italy's Garante fined La Patria 39,000 euros over employee data, according to dataguidance.com, and Poland's UODO fined an entrepreneur PLN 31,507 for failing to cooperate, per CEO Magazyn. MLex reported that Fnac Darty risks a 10 million euro fine in a French cookie case.
Outside Europe, the pattern is enforcement with new teeth attached. South Korea's revised Information and Communications Network Act took effect on 1 October, with penalties of up to 3 percent of revenue for firms with repeat cyber incidents, according to 디지털투데이 and thelec.net. Brazil's regulator fined TikTok owner ByteDance $29.8 million over data belonging to 8 million teenagers in August. In the US, the FTC's independence was ended by a Supreme Court decision in July, which several commentators described as opening an enforcement gap; the FCC has asked the Supreme Court not to review location data fines again, Broadband Breakfast reported on 1 October.
Two things connect these cases. First, the fines that make headlines are rarely the ones that change behaviour fastest; the French tax breach was caught by the attacker's own boast, not by monitoring. Second, the legal exposure is increasingly about what organisations say after an incident. The CFPB disputes that abandoned kit raises breach risk. The French ministry blamed attacker sophistication, and its own agency later documented weak passwords and flat networks. Neither claim is a fine. Both are now on the record.
Elsewhere the enforcement load is shifting sideways. New York's consumer protection office reached a landmark settlement with DoorDash, which Mayer Brown described as confirming an aggressive enforcement posture. Connecticut's privacy and AI compliance landscape is expanding, per jdsupra.com. The European Data Protection Board's fining framework consultation closes against a backdrop of uneven national practice, and Compliance Week noted that regulators want the numbers to converge.
What none of the recent cases settles is the original problem. Data keeps accumulating on hardware, in portals and in message tools long after the organisation has stopped paying attention to it. The CFPB alert, the French audit and the EU's own admission that only 36 percent of sites disclose required data under energy efficiency rules all point the same way: the reporting layer is thinner than the compliance layer assumes.
Sources
15- 01CFPB can't say if data on abandoned office kit is safe, watchdog findsEN
- 02French Tax Data Theft Using Stolen Staff Passwords Went Undetected for Seven WeeksEN
- 03EU accused of hiding environmental impact of data centersEN
- 04EU pressures Big Tech to go green with new data center sustainability labelEN
- 05Globe Telecom bets $1B on data centers as the Philippines positions for hyperscale boomEN
- 06Data Center On-Site Power Brings Pollution Risks Closer to HomeEN
- 07Efforts to Curb Data Center Speculation Gain Ground Across the USEN
- 08ByteDance grabs one-fifth of China's data centre capacity as AI drives infrastructure boomEN
- 09Cloudflare launches Data Platform with bland 'Basin' branding, promise of fewer feesEN
- 10Google thinks SpaceX's Starship has to launch 1,800 times before space data centers get off the groundEN
- 11Meta dodges billions in US taxes by calling its AI data centers experimentsEN
- 12Nebius signs 50MW lease with AIB Data CentersEN
- 13Your LG TV is constantly collecting your data - here's how to stop itEN
- 14Federal Reserve Board issues enforcement action with former employee of Sandy Spring BankEN
- 15Federal Reserve Board issues enforcement actions with former employee of Northstar Bank, former employee of American Express Travel Related Services Company, InEN
All figures and quotations in this text come from the sources listed below.
Content prepared by the editorial team with AI assistance.
Dr. Amara Patel
Comments
0- No comments yet — be the first.